MS Paint vulnerability: Microsoft's fix skips Windows Update, so check your version
CVE-2026-83844 is rated 8.1 and has no known attacks, but the patched Paint build reached the Microsoft Store only this week, weeks after the advisory.
The MS Paint vulnerability, CVE-2026-83844, is a remote code execution flaw rated 8.1 that Microsoft disclosed on October 13. On November 6 Microsoft named Paint build 11.2609.401.0 as the complete fix. It arrives through the Microsoft Store, not Windows Update. Microsoft reports no known attacks.
Microsoft Paint is not an app most people think to patch. The MS Paint vulnerability, tracked as CVE-2026-83844, is why you should. Microsoft says the flaw could let an attacker run code over a network, and on November 6 it named a new build as the complete fix: 11.2609.401.0. Windows Update will not install it. Paint updates through the Microsoft Store, and for weeks the Store had no fixed build to give.
Our 25-second version:
There is no sign of a crisis. Microsoft's advisory says the bug has not been exploited or publicly disclosed, and it rates exploitation as less likely. But checking takes about 20 seconds.
Image: Microsoft (Windows Insider Blog)
What is the MS Paint vulnerability?
Microsoft describes CVE-2026-83844 as an out-of-bounds read that "allows an unauthorized attacker to execute code over a network." An out-of-bounds read means a program reads memory outside the area it was given. Bugs like this can leak data, and Microsoft classes this one as remote code execution, which means an attacker could run their own code on the PC.
Microsoft's scoring explains both the alarm and the calm:
- Base score: 8.1 out of 10, with a severity rating of Important, one step below Critical.
- What an attacker needs: no sign-in and no user interaction, according to the advisory.
- What makes it harder: attack complexity is high. Microsoft says success requires "a deep understanding of the system" and is not guaranteed.
- Current status: exploit code is listed as unproven, and there are no known attacks.
Windows Latest called it a no-click bug, which matches the advisory's "no user interaction" rating.
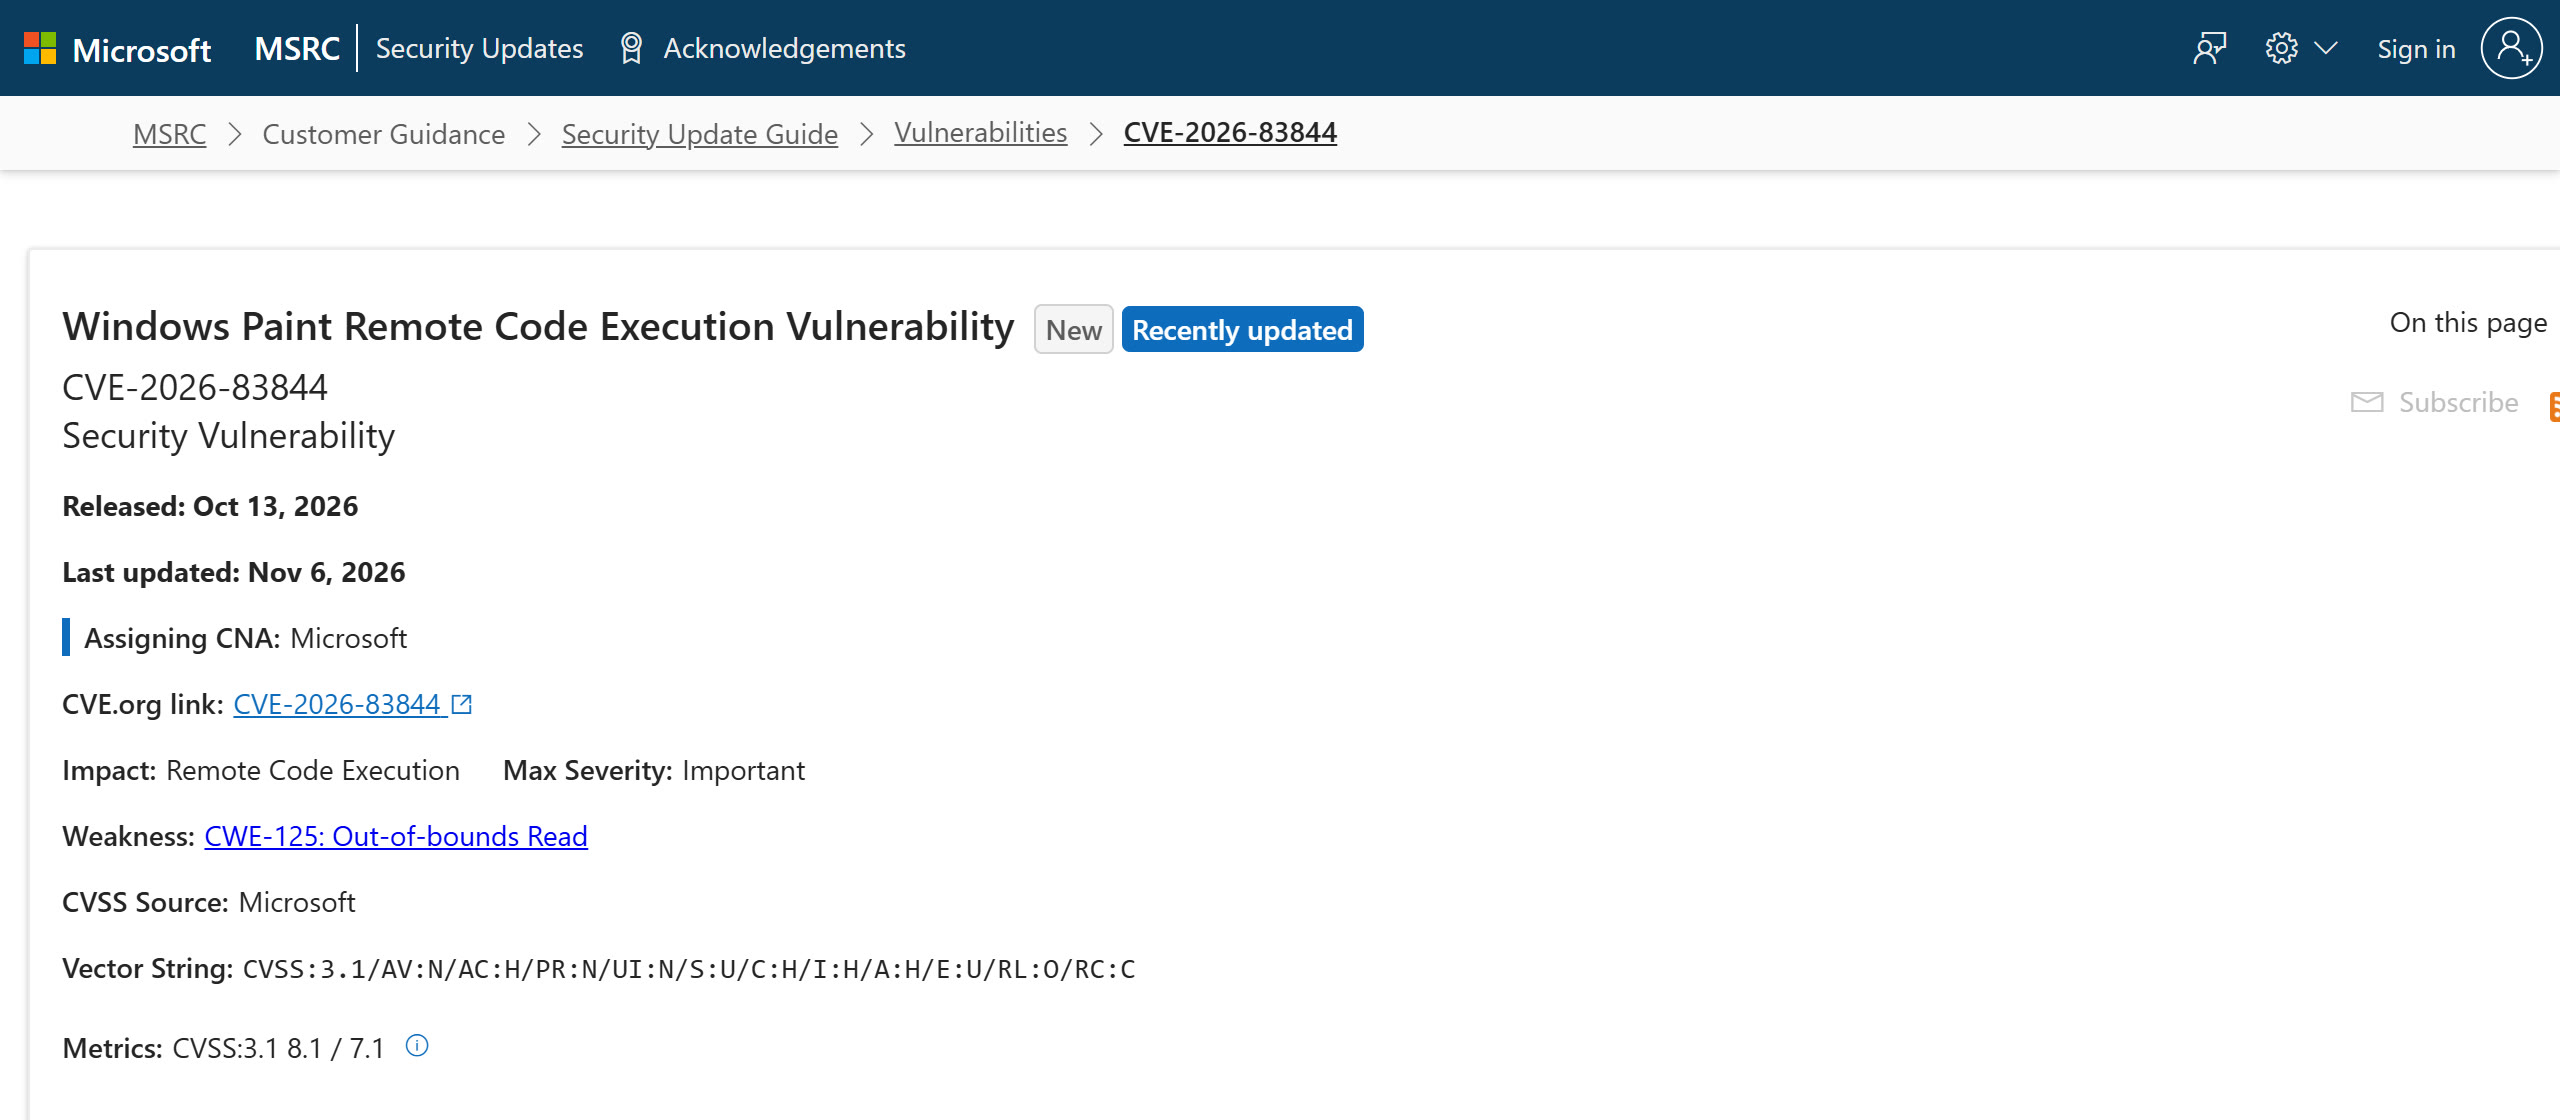
Image: Microsoft Security Response Center (screenshot taken 7 Nov 2026)
How does the attack work?
Nobody outside Microsoft has said. The advisory's FAQ says an attacker could send "a specially crafted packet to an affected service over the network," and it does not name the service. Brian Vitko of device-management firm RFF, who tested the fix, called that an odd description for an image editor and said he does not know the real trigger.
Some early write-ups said a booby-trapped image file sets it off. Microsoft's advisory does not say that, so treat it as unconfirmed.
Why didn't Windows Update fix it?
Paint is a Microsoft Store app, so it updates separately from Windows. A PC with every Windows patch installed can still run an old, unfixed Paint.
The bigger problem was the fix itself. Here is the order of events, from Microsoft's records, Vitko's tests and The Hacker News:
- October 13: Microsoft publishes the flaw and lists 11.2605.91.0 as the fixed build.
- By November 4: Microsoft's security data switches to 11.2609.401.0, with no revision note at the time.
- November 5: Windows Latest finds its own PC on 11.2603.251.0, with Store auto-updates on and nothing offered. Vitko finds that the newest build in the Store in six countries is 11.2605.81.0, which has no fix.
- November 6: the fixed build appears in the Store. The Hacker News finds it is the newest build in all ten countries it checked. Microsoft adds a revision note recommending 11.2609.401.0, and the public CVE record moves to the same number.
That last correction matters for companies. The Hacker News and RFF both warned that the CVE record still used the old cutoff, so a scanner could mark 11.2605.91.0 as safe. The record now lists everything below 11.2609.401.0 as affected, but a scanner working from older data may still use the old number.
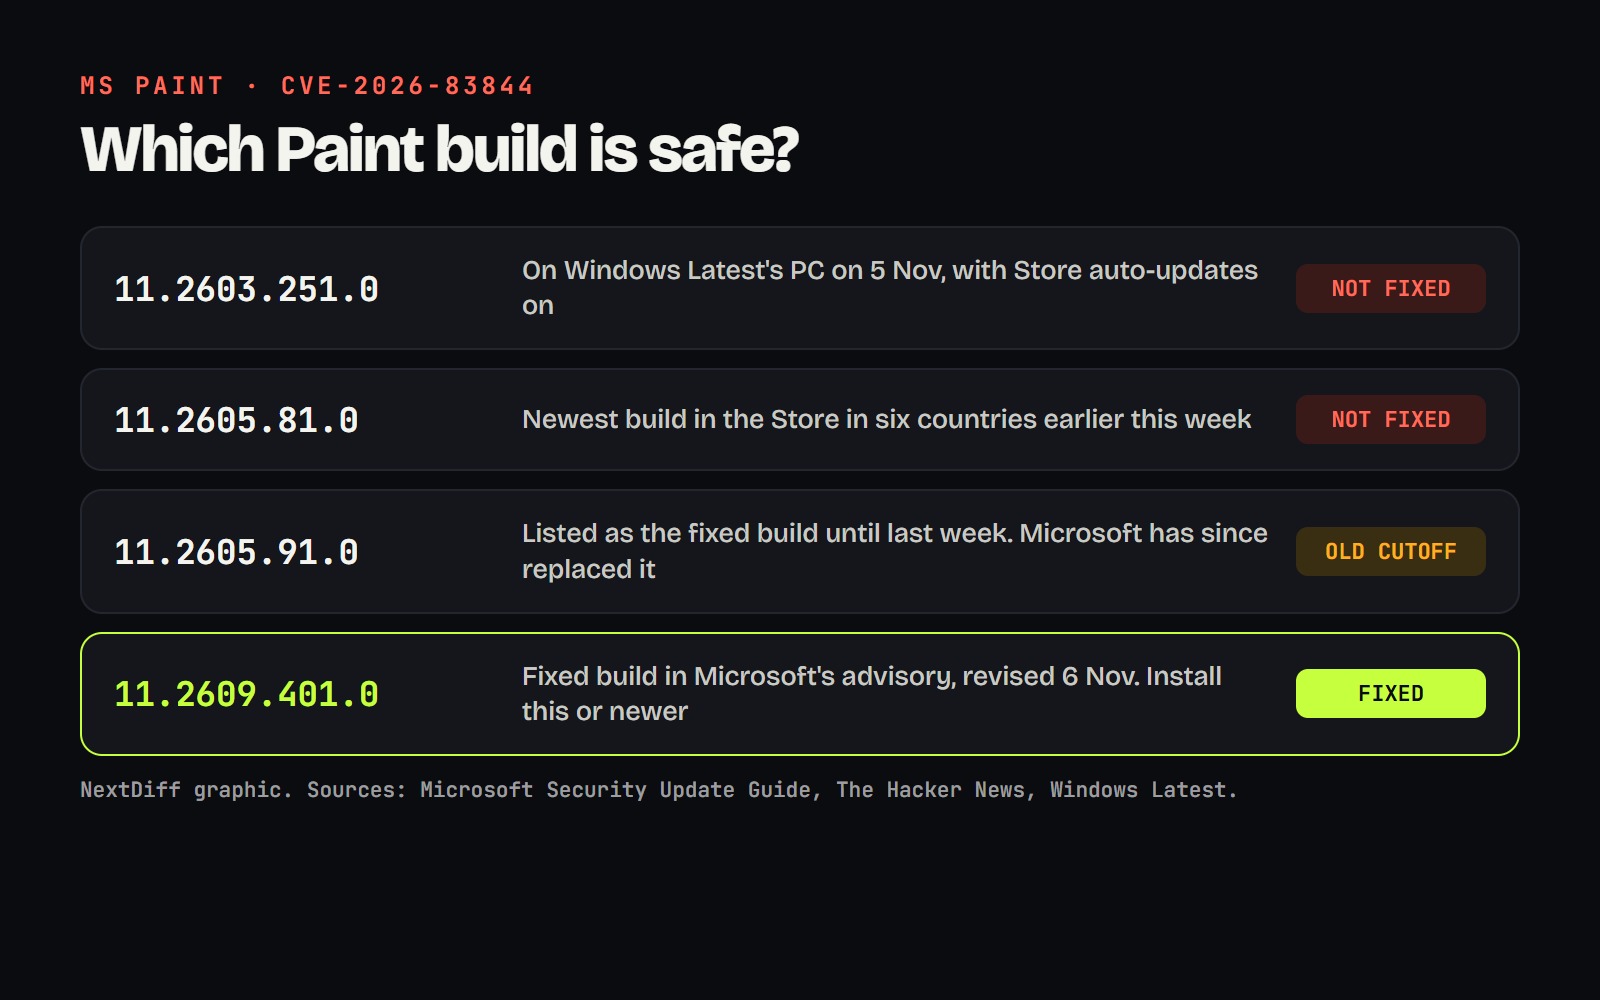
Image: NextDiff (data from Microsoft, The Hacker News, Windows Latest and RFF)
How do I check my Paint version?
Open PowerShell and run the command Windows Latest published:
Get-AppxPackage -Name Microsoft.Paint | Select-Object Name, Version
If the version is 11.2609.401.0 or higher, you have the fix. We ran it on a NextDiff Windows PC this morning, and that PC already had the fixed build, without us updating it by hand:
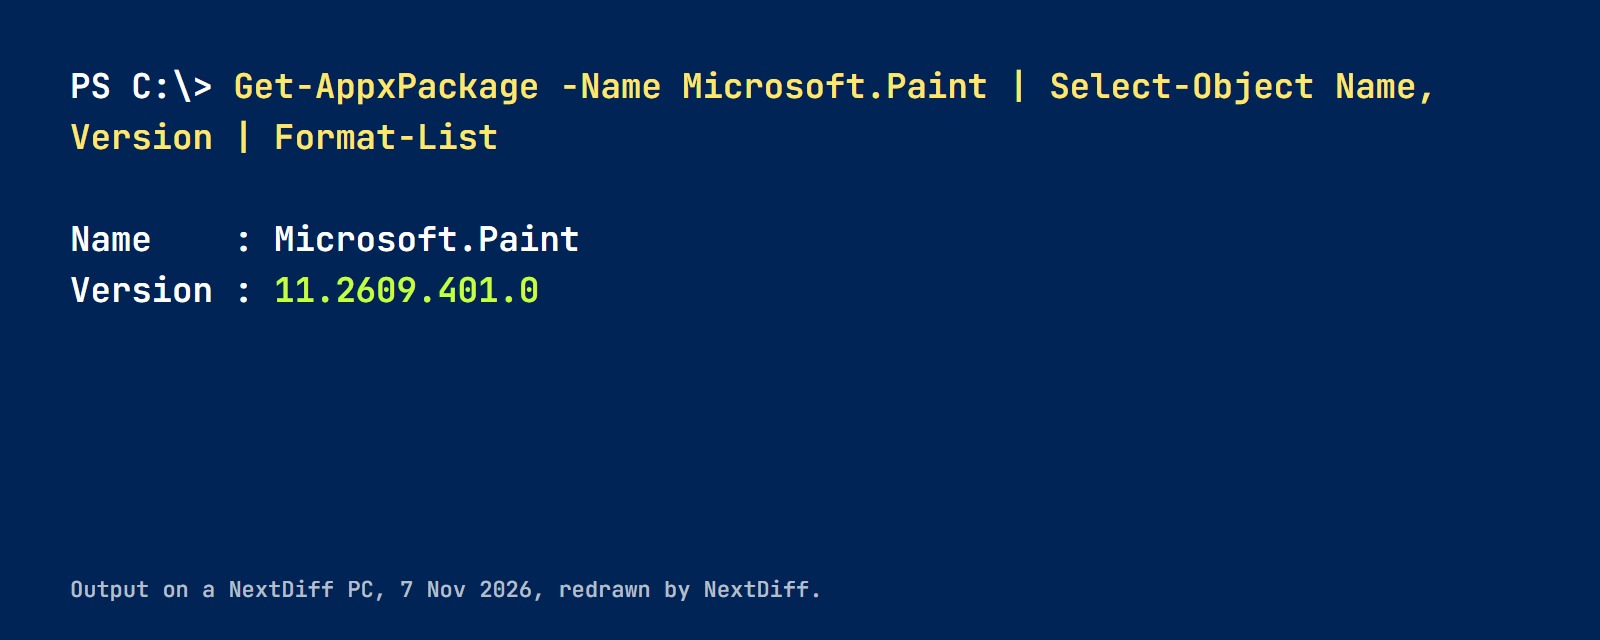
Image: NextDiff (our own PC, 7 Nov 2026)
If yours is older, open Paint in the Microsoft Store or go to the Store's Downloads page and check for updates.
If you run PCs at work: one check is not enough. Store apps install per user, and Windows can also keep a provisioned copy for new accounts. Vitko's commands, run from an elevated PowerShell, cover both:
Get-AppxPackage -AllUsers -Name Microsoft.Paint | Select-Object Version
Get-AppxProvisionedPackage -Online | Where-Object DisplayName -eq 'Microsoft.Paint' | Select-Object Version
Intune and similar tools can trigger the Store update scan across a fleet. The advisory lists no workaround.
Why it matters
The risk from this one bug looks modest for now. The process is the story. Microsoft marks the CVE "customer action required," yet for about three weeks the customers it told to act had nothing to install. Patch dashboards built around Windows Update would also miss it completely, because inbox apps follow a different path.
"Hard to exploit" is also less comforting than it was. Our story on the Linux flaw an AI turned into remote root shows why. Default apps need the same inventory and patch checks as everything else.
What's next?
Microsoft has not said why the fixed build changed or what the "affected service" is. Its Paint release notes for 11.2609.401.0 list faster image loading and clearer errors for damaged files, and they do not mention the security fix. We will update this story if Microsoft explains more or if attacks are reported.
Questions readers ask
- What is the MS Paint vulnerability?
- It is CVE-2026-83844, an out-of-bounds read in Windows Paint that Microsoft says could let an unauthorized attacker run code over a network. Microsoft scores it 8.1 out of 10 and rates it Important.
- Which Paint version fixes CVE-2026-83844?
- Build 11.2609.401.0 or newer. Microsoft's advisory, revised on November 6, 2026, names that build as the complete fix. An earlier build number, 11.2605.91.0, is no longer the one to go by.
- Does Windows Update fix the Paint vulnerability?
- No. Paint is a Microsoft Store app, so it gets the fix through a Store update. A fully updated copy of Windows can still have an old copy of Paint.
- How do I check my Paint version?
- Open PowerShell and run Get-AppxPackage -Name Microsoft.Paint | Select-Object Name, Version. On a shared PC, run an elevated PowerShell with -AllUsers, because each user account has its own copy of Paint.
- Is the MS Paint vulnerability being exploited?
- Microsoft's advisory says no, and it lists the flaw as not publicly disclosed. The Hacker News also found it missing from the CISA Known Exploited Vulnerabilities catalog on November 6.
+ Sources
- Microsoft Security Response Center: CVE-2026-83844 advisory
- The Hacker News: Microsoft Paint RCE fix now available, but Windows Update won't deliver it
- Windows Latest: Windows 11's Paint has a no-click hacking bug
- RFF, Brian Vitko: Windows Paint CVE-2026-83844 store fix test
- CVE.org: CVE-2026-83844 record
- Microsoft Learn: Paint release notes for Windows Insiders
- Microsoft Store: Paint
+ Rate this story
Get stories like this on your phone, the minute they drop.
 Scan with your Android phone
The Weekly Diff launches soon.
Subscribe on YouTubeKeep reading